

Entrust adds CBOM tools to Cryptographic Security Platform
Fri, 2nd Oct 2026 (Today)
Entrust has expanded its Cryptographic Security Platform with new Cryptographic Bill of Materials import and export functions, aimed at helping organisations build more complete inventories of cryptographic assets.
The update also extends the platform's governance, certificate automation and post-quantum features as companies face tighter oversight of software components, shorter certificate lifecycles and a growing number of machine identities.
The move comes as regulators and security agencies place greater emphasis on visibility into software components and dependencies. In Australia, updated guidance from the Australian Signals Directorate's Australian Cyber Security Centre on the minimum elements of a Software Bill of Materials has added to broader pressure on organisations to map technology dependencies more closely.
The new import and export functions are designed to help security teams connect cryptographic inventories with the systems and applications that rely on them. That includes keys, certificates and secrets, as well as their relationships to the broader technology estate.
For security teams, the goal is to move beyond basic discovery. By linking inventory data to governance and operational workflows, organisations can identify cryptographic assets that may be vulnerable or non-compliant, assess which systems depend on them and prioritise remediation.
The platform is now available both as a service and for on-premises deployment, giving customers a choice between hosted and locally managed setups, including for organisations with security or data sovereignty requirements.
Inventory pressure
Cryptographic inventories have become more important as businesses manage growing numbers of digital certificates across public and private public key infrastructure environments. At the same time, organisations are preparing for the eventual shift to post-quantum cryptography, which will require a detailed understanding of where existing algorithms and certificates are used.
Entrust is also adding Ansible-based certificate lifecycle automation functions to help teams deploy and manage certificates across more customised environments, while reducing manual work and limiting service disruption.
Another part of the update adds support for composite algorithms and SPIRE-based identity functions. These are intended to help organisations plan phased post-quantum migration and support identities for AI agents and other non-human workloads.
Industry and regulatory developments have made this inventory work more urgent. International policy changes have pushed software producers and operators to improve visibility over components and dependencies, while critical infrastructure operators and financial institutions face growing scrutiny over operational resilience and cyber risk.
For Australian government bodies and critical infrastructure operators, understanding where cryptographic material is deployed may also shape how future remediation is prioritised. Mapping the use of keys, certificates and algorithms can show which applications and services would be affected by cryptographic changes.
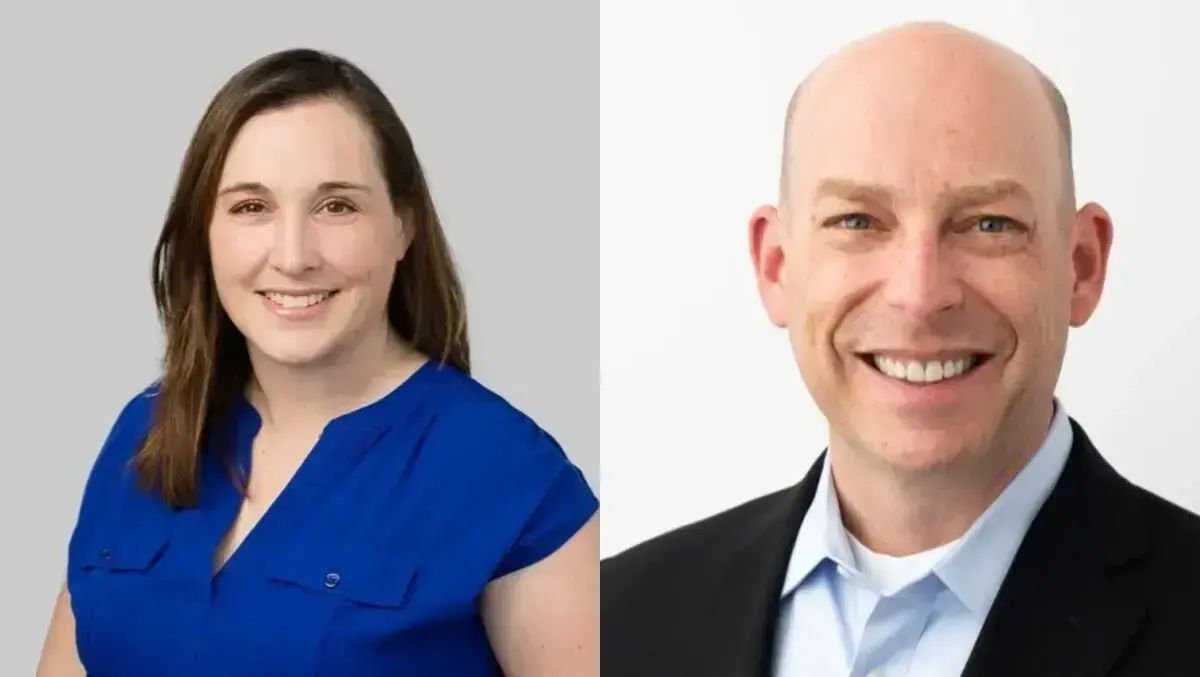
Michael Klieman, Global Vice President of Product Management at Entrust, said the company sees CBOM data as useful only when it is linked to operational decisions.
"A CBOM is more than a static inventory," said Michael Klieman, Global Vice President of Product Management at Entrust.
"Security teams need to connect CBOM data with the systems and applications that depend on cryptography, understand where risk is concentrated and determine what actions to take next. Adding CBOM support to the platform helps organisations move from documenting cryptographic assets to actively governing and securing them."
Analysts have also pointed to the growing burden on security teams as the number of machine identities rises. That trend is being compounded by AI-related workloads, which introduce additional authentication and trust requirements across systems.
Jennifer Glenn, Research Director for Information and Data Security at IDC, said the challenge is no longer just visibility but operational follow-through.
"Knowing where cryptography lives isn't enough anymore. The number of certificates and other cryptographic material is growing rapidly. Machine and AI identities are multiplying, and the deadline to transition to post-quantum algorithms is closing in. Security teams cannot treat cryptographic inventory as a static exercise. Organisations that connect cryptographic inventory, governance, automation and post-quantum readiness will be better positioned to manage crypto-agility as standards evolve."